위협 노출 진단 서비스 Threat Exposure Diagnosis Service
withREX는 Shadow IT, Shadow API를 포함한 모든 공격 표면을 식별·목록화하고,
실제 위협 노출을 정량화하여 데이터 기반 보안 의사결정을 지원하는 서비스입니다.
withREX identifies and inventories all attack surfaces including Shadow IT and Shadow API,
quantifies actual threat exposure, and supports data-driven security decision-making.
Background
현재 네트워크에 보안팀도 모르는 자산이 몇 개나 숨어 있습니까?
그리고 그 자산이 지금 이 순간 위협에
노출되어 있다면?
How many assets are hidden in your network that even your security team doesn't know about?
And what if those assets are exposed to threats
at this very moment?
공격 표면의 확장은 곧 위협의 증가를 의미합니다.
단순 관리를 넘어, 실제 위협에 노출된 '위험 자산'을
식별하고 제거해야 합니다.
An expanding attack surface means an increasing threat landscape.
Beyond simple management, you must identify and eliminate
'at-risk assets' actually exposed to threats.
Threat Exposure Diagnosis withREX
네트워크 자산 가시성 확보부터 위협 노출 진단까지,
withREX는 Shadow IT/API Scanning 방식으로
즉시 공격 표면을 탐지하고 위협 노출을 진단하는 서비스입니다.
From securing network asset visibility to diagnosing threat exposure,
withREX detects attack surfaces instantly using Shadow IT/API Scanning
and diagnoses threat exposure as a service.
위협 노출 관리 진단 서비스Threat Exposure Management Diagnosis
withREX
withREX는 공격 표면 탐색을 기반으로 위협 노출을 정량화하는 데이터 기반 진단 서비스입니다. withREX is a data-driven diagnosis service that quantifies threat exposure based on attack surface exploration.
Key Features
주요 기능Key Features
주요기능Feature 01
Shadow IT, Shadow API 위협 노출 제거Shadow IT & Shadow API Threat Exposure Elimination
  • 네트워크 기반 스캐닝으로 미관리 IT 자산 탐지Network-based scanning to detect unmanaged IT assets
  • ShadowIT & API 포함 공격 표면 완전 식별Complete identification of attack surface including Shadow IT & APIs
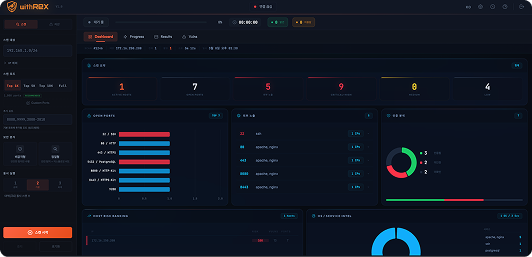
  • IP, 도메인, Open Port, OS 등 상세 정보까지 목록화Inventory of detailed information including IP, domain, open ports, OS
  • 위협 진단을 위한 기초 데이터 확보Securing foundational data for threat diagnosis
주요기능Feature 02
AI 기반 정밀 자산 식별AI-Based Precise Asset Identification
  • 패킷 응답 특성(TTL, Window Size 등) AI 분석으로 OS FingerPrintingOS fingerprinting through AI analysis of packet response characteristics (TTL, Window Size, etc.)
  • Shadow IT/API Scanning 방식으로 OS 유형 및 커널 버전 식별Identifying OS type and kernel version via Shadow IT/API Scanning
  • 취약점 매핑과 위험도 평가를 위한 자산 특성 정교화Refining asset characteristics for vulnerability mapping and risk assessment
  • 운영 중단 없는 안전한 자산 프로파일링Safe asset profiling without operational disruption
주요기능Feature 03
위협 노출 정량화 및 진단Threat Exposure Quantification & Diagnosis
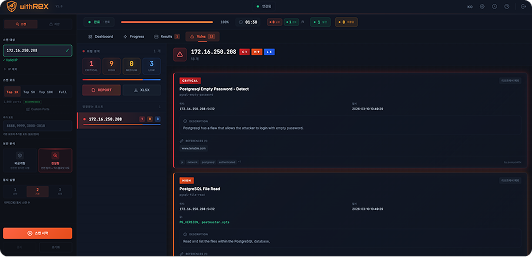
  • CVE 데이터베이스 기반 실제 취약점 자동 탐지 및 분석Automatic detection and analysis of actual vulnerabilities based on CVE database
  • 자산별 위험도 분류 및 위험 우선순위 도출 (Critical / High / Medium / Low)Per-asset risk classification and priority derivation (Critical / High / Medium / Low)
  • 인증 누락, 관리 페이지 노출, API 취약점 등 보안 설정 오류까지 진단Diagnosis including missing authentication, exposed admin pages, and API vulnerabilities
주요기능Feature 04
규제 대응 리포트 및 조치 가이드Regulatory Compliance Reports & Remediation Guides
  • 발견된 전체 자산 현황 및 위협 노출 현황 시각화 리포트Visualized reports on all discovered assets and threat exposure status
  • 위협 노출 현황 및 위험도 분석 (Critical / High / Medium / Low)Threat exposure status and risk analysis (Critical / High / Medium / Low)
  • 자산 및 취약점별 조치 권고사항 가이드 제공Remediation recommendation guides per asset and vulnerability
Process
위협 노출 진단 서비스 프로세스Threat Exposure Diagnosis Process
STEP 01 Scoping
범위 설정Scope Definition
  • 고객 비즈니스 환경 및 보호 대상 자산 분석Analysis of customer business environment and assets to be protected
  • 운영 영향도를 최소화한 안전한 Shadow IT/API Scanning 진단 정책 수립Establishing safe scanning policies minimizing operational impact
  • N2SF, 범부처 정보보호 종합대책 등 규제 및 기관 정책 반영Reflecting regulatory policies including N2SF and National Cybersecurity Master Plan
STEP 02 Discovery
자산 탐색Asset Discovery
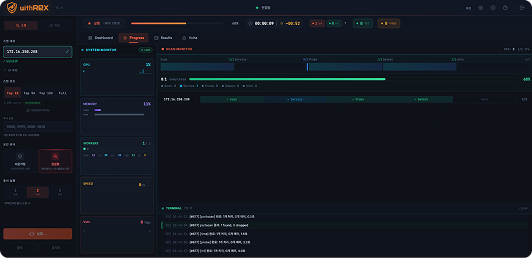
  • Shadow IT/API Scanning으로 Shadow IT & API 포함 공격 표면 탐색Attack surface exploration including Shadow IT & APIs via Shadow IT/API Scanning
  • AI 기반 OS Fingerprinting으로 OS 유형 및 버전 등 자산 정보 상세 식별Detailed asset identification via AI-based OS Fingerprinting
  • IP, 도메인, Open Port등 자산 구성요소 목록화Inventory of asset components including IP, domain, and open ports
STEP 03 Assessment
위험 평가Risk Assessment
  • CVE, 인증 미적용, 관리 페이지 노출, API 취약점 등 실제 취약점 진단Diagnosis of actual vulnerabilities including CVE, missing auth, exposed admin pages, API vulnerabilities
  • 자산별 위험도 정량화 및 분류 (Critical / High / Medium /Low)Per-asset risk quantification and classification (Critical / High / Medium / Low)
  • 데이터 기반 조치 권고사항 및 의사결정 지원 리포트 제공Data-driven remediation recommendations and decision-support reports
Impact of Introduction
기대 효과Expected Benefits
전사 IT 자산의 가시성 확보와 데이터 기반의 의사결정으로
선제적 보안 체계를 구축합니다
Build a proactive security framework
through enterprise IT asset visibility and data-driven decision-making
전사 IT 자산 가시성 확보 및
보안 사각지대 제거
Enterprise IT Asset Visibility
& Security Blind Spot Elimination
Visibility
  • Shadow IT, Shadow API 포함 실제 운영 자산을 식별하여 관리 사각지대 제거Eliminating management blind spots by identifying actual operational assets including Shadow IT and Shadow APIs
  • 미관리 자산을 통한 침해 사고 가능성 차단Blocking the possibility of breaches through unmanaged assets
  • 클라우드 및 임시 자산 등 동적 환경의 보안 위험 요소 조기 발견Early discovery of security risks in dynamic environments including cloud and temporary assets
데이터 기반
위협 노출 관리 체계 구축
Building a Data-Driven
Threat Exposure Management Framework
Risk Management
  • 위험도 기반 정량적 데이터로 객관적 의사결정 가능Objective decision-making enabled by risk-based quantitative data
  • 자산별 위협 노출 수준 데이터를 통한 조치 우선순위 자동 도출Automatic derivation of remediation priorities through per-asset threat exposure level data
  • 에이전트 설치 없이 즉시 수집한 위협 노출 데이터로 신속한 대응 체계 구축Building rapid response frameworks with instantly collected agentless threat exposure data
데이터 기반 운영 효율성 및
규제 대응 완성
Data-Driven Operational Efficiency
& Regulatory Compliance
Compliance & Optimization
  • 위험도별 조치 우선순위로 막연한 불안이 아닌 정량적 의사결정 가능Quantitative decision-making through risk-level remediation priorities
  • 범부처 정보보호 종합대책의 'IT 자산 전수조사' 요건 대응Meeting the 'Complete IT Asset Survey' requirement of the National Cybersecurity Master Plan
  • N2SF 가이드라인의 '망 위협 탐지' 필수 항목 대응Meeting the mandatory 'Network Threat Detection' item of the N2SF guideline
withREX 위협 노출 진단 서비스는
Shadow IT & Shadow API를 포함한
모든 자산의 실제 위협 노출 수준을 정량화하여
데이터 기반 의사결정 체계를 구축
합니다.
The withREX Threat Exposure Diagnosis Service
quantifies the actual threat exposure level of all assets
including Shadow IT & Shadow APIs,
building a data-driven decision-making framework
.