자산 및 보안 취약점 통합관리 솔루션 Integrated Asset & Security Vulnerability Management Solution

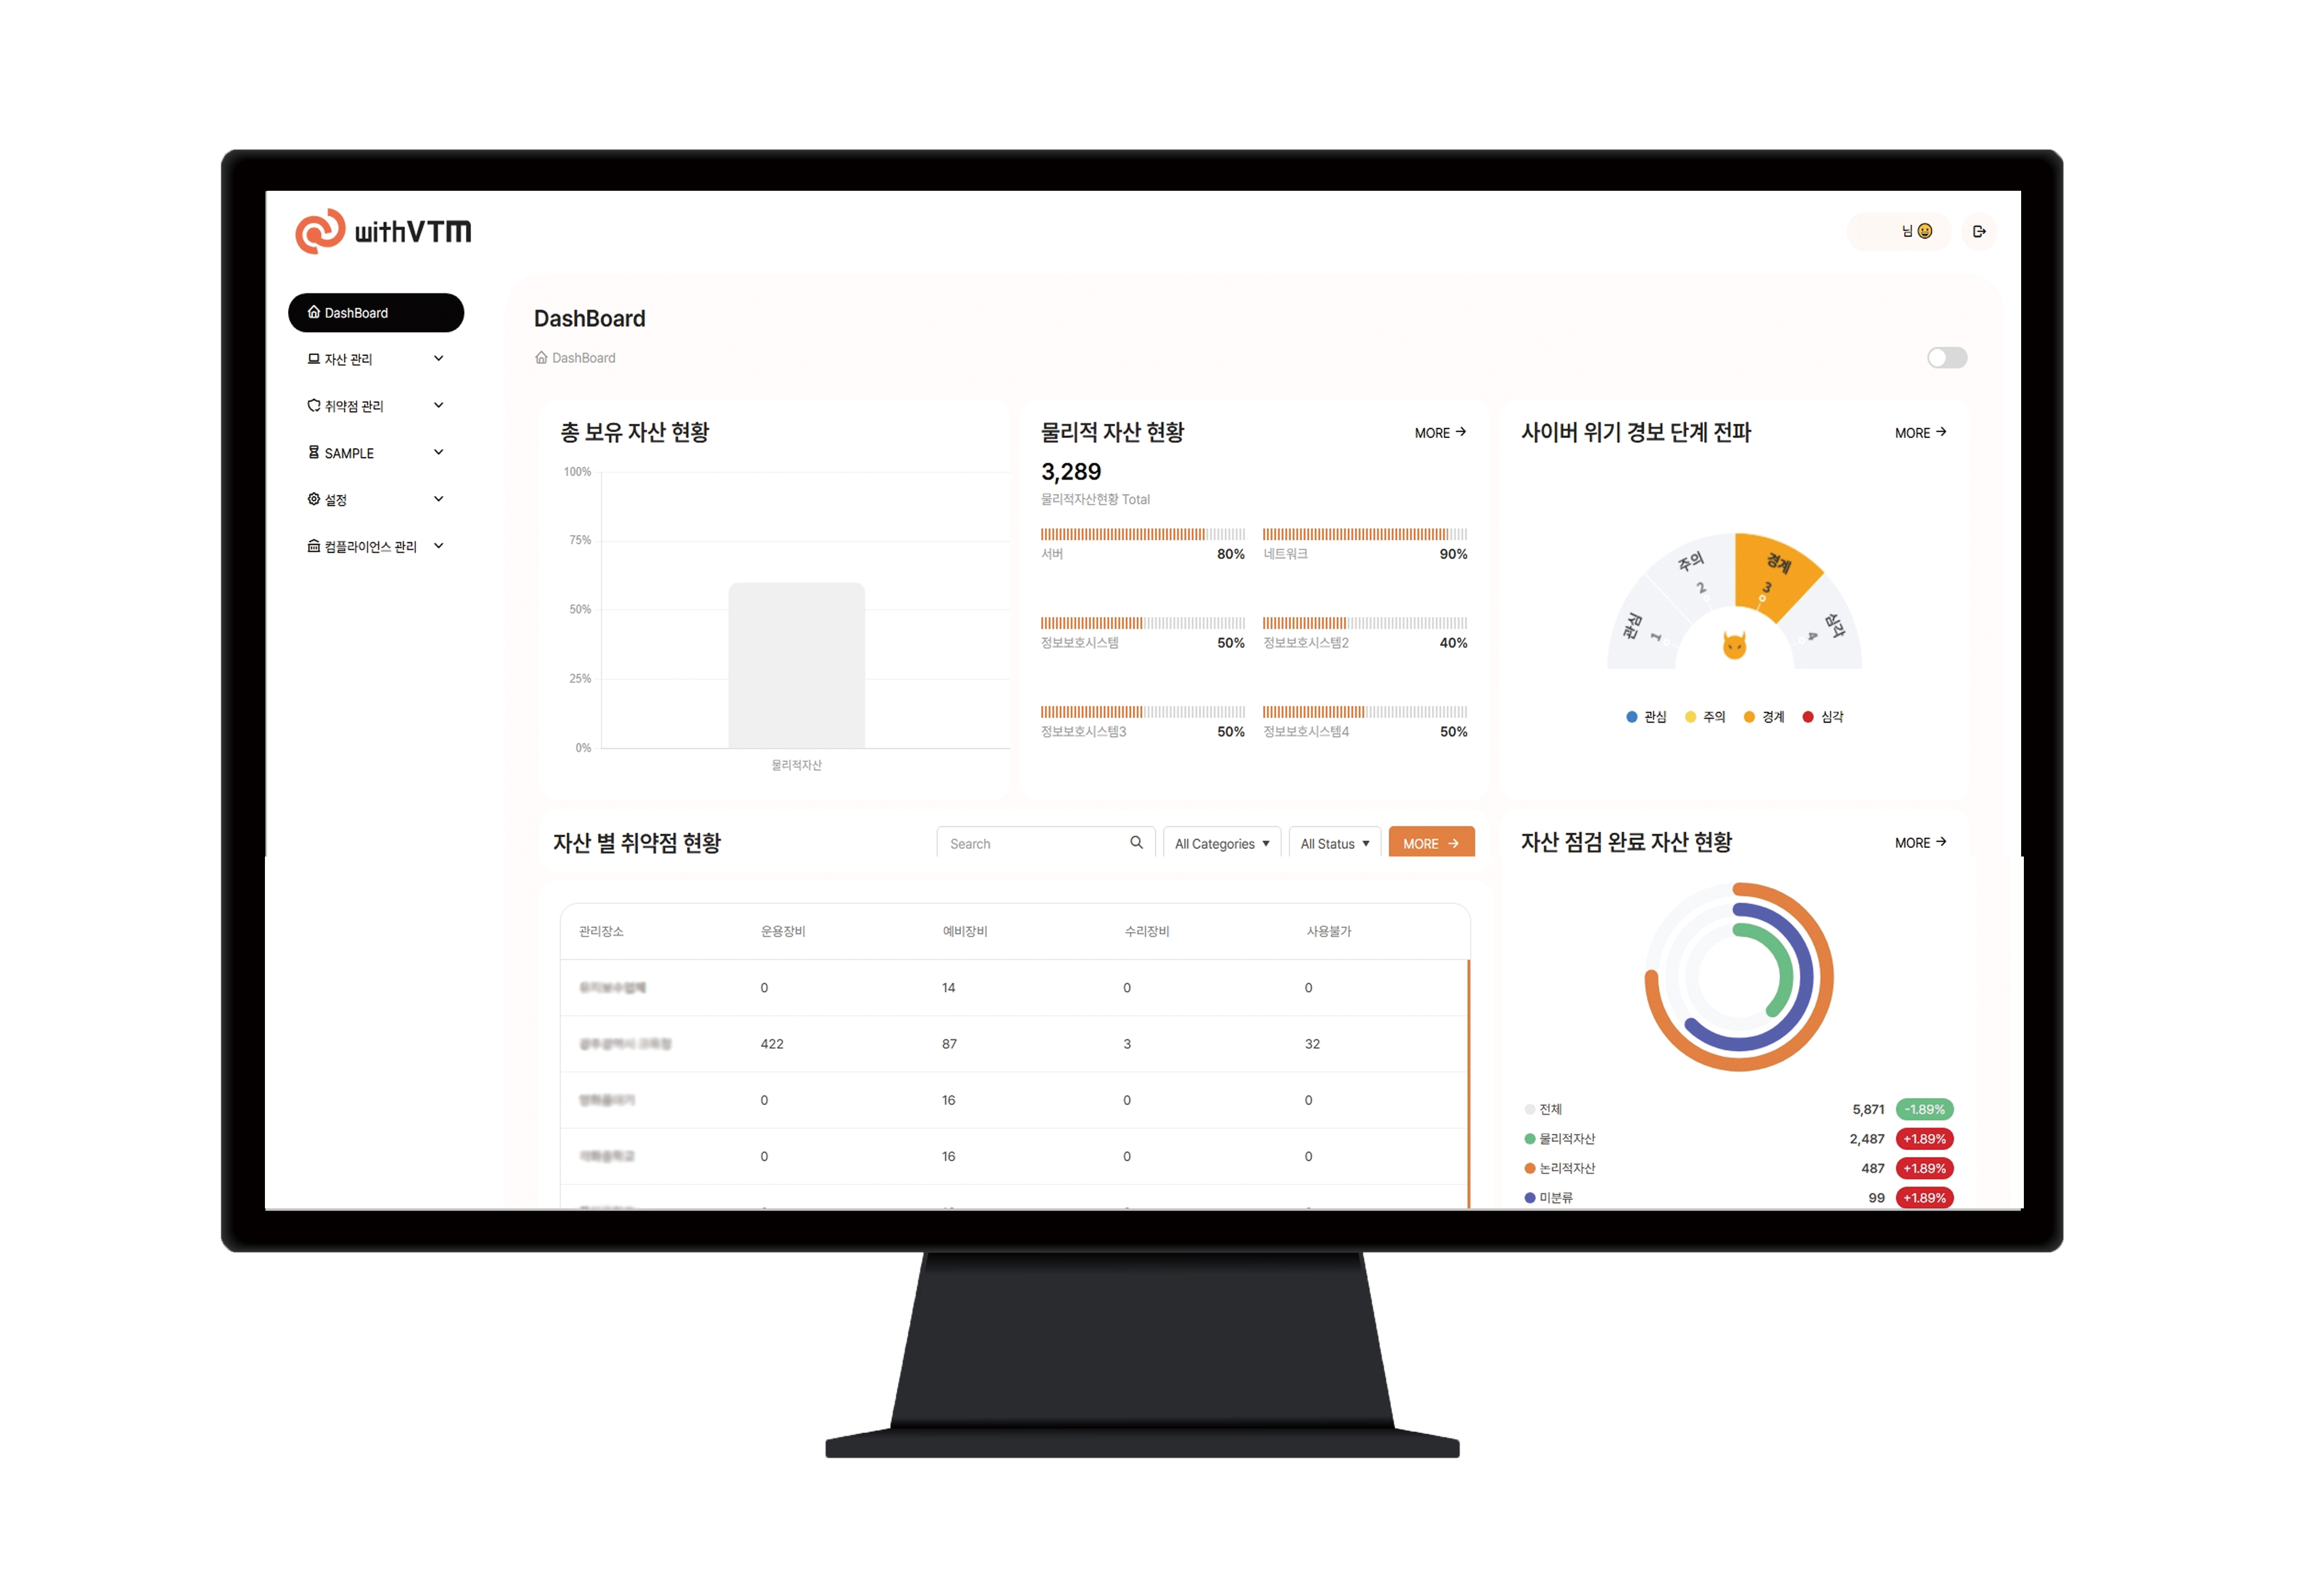
withVTM은 내부 자산부터 알려지지 않는 외부 자산까지 모든 자산을 식별하고 관리하며, 발견된 자산에 대한 취약점을 지속적으로 관리합니다. 또한, AI 기반 위험도 평가로 "무엇을 먼저 조치해야하는지" 명확한 우선순위를 제시하는 자산・취약점 통합 관리 솔루션입니다. withVTM identifies and manages all assets—from internal to unknown external assets—and continuously monitors vulnerabilities across them. Powered by AI-based risk assessment, it provides clear prioritization of 'what to fix first,' delivering a comprehensive asset and vulnerability management solution.
Background
자산 및 보안 취약점 관리가 필요한 이유 Why Asset & Security Vulnerability Management Matters
IT 자산은 급속히 증가하고 있지만, 보안 관리 체계는 이를 따라잡지 못해
조직들이 보이지 않는 위험에 노출되고 있습니다.
IT assets are growing rapidly, but security management frameworks struggle to keep pace,
leaving organizations exposed to invisible risks.
보호해야 할 대상을 정확히 모르면, 보안은 시작조차 할 수 없습니다.
withVTM은 바로 '무엇을 보호해야 하는가' 라는 질문에 명확한 우선 순위를 제시합니다.
If you don't know exactly what to protect, security can't even begin.
withVTM provides a clear answer to the fundamental question: 'What must be protected—and what first?'
withVTM
자산 및 보안 취약점 통합 관리 솔루션 Integrated Asset & Security Vulnerability Management Solution
  • 보안 중심 자산 관리Security-Centric Asset Management
    • ShadowIT 포함 전사 자산 가시성 확보Full enterprise asset visibility including Shadow IT
    • 자산별 중요도 기반 인벤토리 구축Asset inventory built on criticality-based classification
  • AI 기반 VRS 우선순위 스코어링AI-Based VRS Priority Scoring
    • 취약점 진단 및 위험도 기반 대응 우선순위 제공Vulnerability diagnosis with risk-based response prioritization
    • 자산 중요도 × 취약점 점수 × 위협 정보를 AI가 종합 분석하여 고위험 자산 선별AI comprehensively analyzes asset criticality × vulnerability score × threat intelligence to identify high-risk assets
  • 다양한 Third Party 솔루션 연동Diverse Third-Party Solution Integration
    • 상용, 오픈소스 스캐너 연동Integration with commercial and open-source scanners
    • ITSM, 전자결재, NAC 등 연동 통한 유연한 운영 환경 구성Flexible operations via ITSM, e-approval, NAC and other integrations
  • 감사대응Compliance & Audit Response
    • 점수제 기반 평가 및 사전 대응 기능Score-based evaluation with proactive compliance features
    • 감사 대응 및 이행 결과 보고서 제공Automated audit response and compliance result reports
withVTM
PROCESS
자산 식별 및
목록화
Asset Discovery
& Inventory
STEP 01
  • ShadowIT 포함 전사 자산 탐지Enterprise asset detection including Shadow IT
  • AI 기반 OS 및 오픈 포트 자동 식별AI-based automatic OS and open port identification
  • 어플리케이션 버전, 포트, 서비스 정보 수집Collection of application version, port, and service information
  • 상세 소프트웨어 인벤토리 자동 구성Automatic construction of detailed software inventory
자산 등급화 및
중요도 평가
Asset Classification
& Criticality Assessment
STEP 02
  • ITSM·DB·스캔정보·설문지 기반 자산 정보 수집Asset information collection based on ITSM, DB, scan data, and surveys
  • 자산 가치와 중요도를 위험 평가에 반영Incorporating asset value and criticality into risk assessment
취약점 분석 및
AI 기반 위험도 스코어링
Vulnerability Analysis
& AI Risk Scoring
STEP 03
  • 자산별 CVE 취약점 매핑 및 진단Per-asset CVE vulnerability mapping and diagnosis
  • CCE 보안 설정 오류 정밀 점검Precise inspection of CCE security misconfigurations
  • 자산 중요도와 취약점 정보 종합하여 위험도 평가Risk evaluation combining asset criticality and vulnerability data
  • AI 기반 VRS 위험도 스코어링 통한 대응 우선순위 제공Response prioritization through AI-based VRS risk scoring
통합 관리 및
대응 자동화
Integrated Management
& Response Automation
STEP 04
  • 위험도 기반 체계적 취약점 관리Systematic vulnerability management based on risk level
  • 조치 이력 추적 및 지속적 모니터링Remediation history tracking and continuous monitoring
  • 점검 결과·조치 이력 기반 감사자료 자동 생성 및 관리로 컴플라이언스 대응 지원Compliance support through automated audit material generation based on inspection and remediation history
Impact of Introduction
기대효과Expected Benefits
보안 사각지대 해소 및 보안사고 예방Eliminating Security Blind Spots & Preventing Incidents
  • Shadow IT 등 미관리 자산을 자동 발견하여 숨겨진 공격 경로 차단Automatically discovering unmanaged assets like Shadow IT to block hidden attack vectors
  • 노출된 자산의 위험요소를 선제적으로 식별해 보안 사고 가능성 최소화Proactively identifying risk factors in exposed assets to minimize the likelihood of security incidents
신뢰도 높은 자산 기반 보안 운영 환경 구축Building a Reliable Asset-Based Security Operations Environment
  • 상세 자산 인벤토리를 기반으로 전사 자산 및 취약점을 통합적으로 관리Managing enterprise-wide assets and vulnerabilities comprehensively based on detailed asset inventory
  • 자산 변동 사항을 지속적으로 반영하여 최신 보안운영 체계 유지Maintaining up-to-date security operations by continuously reflecting asset changes
취약점 평가 관리를 통한 보안 운영 안정성 강화Strengthening Security Operations Stability Through Vulnerability Management
  • 취약점(CVE)·설정오류(CCE) 현황을 지속적으로 관리하여 안정적 운영 확보Ensuring stable operations through continuous management of CVE vulnerabilities and CCE misconfigurations
  • AI 기반 VRS 스코어링으로 현실적인 위험도 산정 및 대응 우선순위화Realistic risk assessment and response prioritization through AI-based VRS scoring
보안 거버넌스 컴플라이언스 시스템 구축Building a Security Governance & Compliance System
  • 강화되는 보안 규제 요구사항에 최적 대응(범부처 정보보호 종합 대책, 국가망 보안체계 N2SF 등)Optimal response to evolving security regulations (National Cybersecurity Master Plan, N2SF, etc.)
  • 실태평가·컴플라이언스 감사 대응을 위한 증적 관리 체계 구축Building an evidence management system for status assessments and compliance audits
withVTM은 전사 자산·취약점·감사 정보를 통합해
보안 체계를 강화하고 안정적인 시스템 운영 환경을 제공합니다.
withVTM integrates enterprise-wide asset, vulnerability, and audit information
to strengthen your security framework and ensure stable system operations.